Exoscale is a cloud platform with its center of gravity in Switzerland and Austria. Selling points for Exoscale are engineering mindset, Open Source culture and products, data security, GDPR compliance, data privacy and good geographical distribution of data centres.
Features & Services
The service portfolio of Exoscale is a straightforward set of IaaS services. All of the services are built on raw Open Source products, which means that lock-in with Exoscale is low. On the other hand, a lot may have to be built on top of the basic building blocks provided by Exoscale.
The DBaaS services of Exoscale seem to be powered by Norwegian Aiven, a mature cloud-scale platform for managed Kafka and various other managed databases.
Developer Experience
There are several ways to interact with the Exoscale platform.
Console
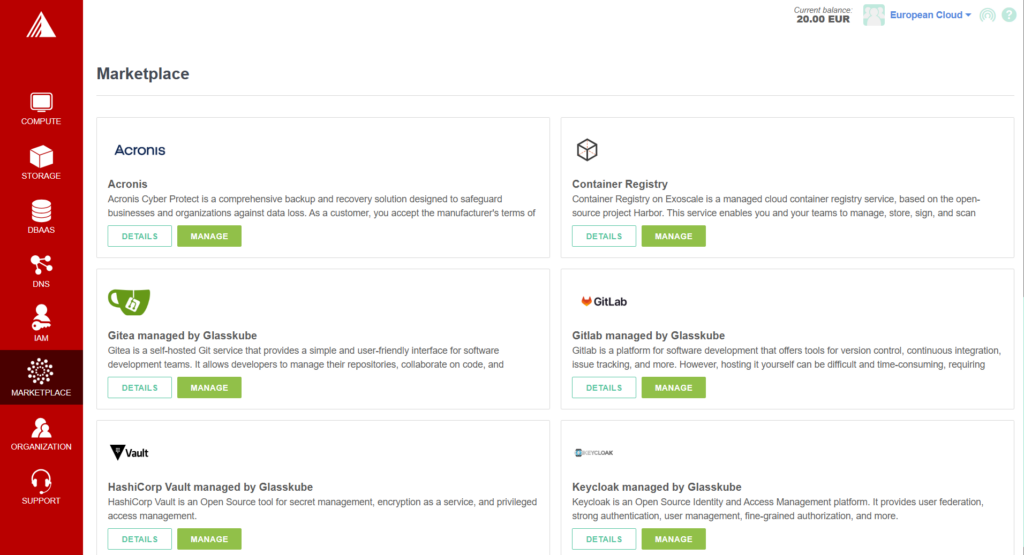
The Exoscale Console is well-ordered and easy to get around.
API
Behind libraries, CLI, Terraform and all other ways to interact with Exoscale lies the Exoscale API.
CLI
The Exoscale Command Line Interface (CLI) covers the whole surface and is well-structured and easy to understand and work with.
For more information, check the documentation of the Exoscale CLI.
Terraform
The Exoscale Terraform provider is published in the Terraform Registry, along with it’s documentation.
The first steps to set up the Exoscale Terraform provider with credentials and a container for the Terraform state are described in the Exoscale Terraform provider documentation.
SDKs
There is a larger-than-average number of official libraries to work with Exoscale resources.
| egoscale | The Golang library for Exoscale. | egoscale on GitHub |
| python-exoscale | Python bindings for the Exoscale API. | python-exoscale on GitHub |
| exoscale-sdk-java | Java API for Exoscale services. | exoscale-sdk-java on GitHub |
| pulumi-exoscale | Pulumi provider to manage Exoscale resources. | pulumi-exoscale on GitHub |
| crossplane-exoscale | Crossplane provider to manage Exoscale resources. | crossplane-exoscale on GitHub |
Sovereignty Assessment
For the sovereignty assessment, we are following the EU's Cloud Sovereignty Framework. It defines 8 sovereignty objectives and makes sovereignty measurable and quantifiable.
Disclaimer: this assessment is conducted as an outside-in analysis, based on public information and, for some questions, educated guessing. The results may be factually wrong and in no way replace your own due diligence.
Overall Score
60.7 %
SEAL Level
SEAL 1
- Provider
- Exoscale
- Framework
- Initial framework from the Sovereignty assessment calculator annex (v1.0)
- Assessment date
- 2. September 2026
- Overall score
- 60.7 %
- SEAL level
- SEAL 1
SOV-1 — Strategic Sovereignty
Strategic sovereignty captures the degree to which a cloud provider (or technology actor) is anchored within the European Union/EEA legal, financial, and industrial ecosystem. It assesses ownership stability, governance influence, and alignment with EU strategic priorities.
Weight 20%
Selected answer: 2. Mostly outside the EU Value 41 SEAL 1
Notes: Operating entity Akenes SA is Swiss (non-EU/EEA). Intermediate parents (A1 Digital, Telekom Austria) are EU, but ultimate control via América Móvil (Mexico) places decision authority outside EU.
Evidence
- A1 Group — Investor Relations / Share Page other 3. September 2026
Official A1 Group investor relations page showing shareholder structure: América Móvil (~56-58%) and ÖBAG (~28%), with ISIN AT0000720008 listed on Vienna Stock Exchange.
Relevance: Confirms the majority shareholder is América Móvil (Mexican), not EU-based. While Telekom Austria is listed in Austria, ultimate control sits outside the EU, impacting strategic sovereignty assessment. - A1 Telekom Austria Group — Wikipedia other 3. September 2026
Wikipedia article detailing América Móvil's ~58% majority stake in Telekom Austria and the 2014 syndicate agreement giving it controlling influence.
Relevance: Establishes that ultimate decision-making authority rests with América Móvil (Mexico), a non-EU entity, through majority shareholding and syndicate agreement — placing corporate control outside EU jurisdiction. - About Us | Exoscale European Cloud Services other 3. September 2026
Official Exoscale page confirming Akenes SA (Switzerland) is the legal entity, part of A1 Digital and A1 Telekom Austria Group.
Relevance: Confirms operating entity is Swiss (non-EU/EEA) and part of the A1 ownership chain. Switzerland is not in EU/EEA, so direct legal entity control is outside EU jurisdiction.
All possible answer options (4)
- 1. Entirely outside the EU (value 0.00, SEAL 1)
- 2. Mostly outside the EU (value 41.00, SEAL 1) ✓
- 3. Mostly within the EU (value 83.00, SEAL 3)
- 4. Entirely within the EU (value 125.00, SEAL 4)
Selected answer: 5. Very unlikely Value 125 SEAL 4
Notes: ÖBAG's 28% stake with veto rights (via Austria Package) and AMX's private (non-sovereign) ownership make transfer to a non-EU sovereign entity very unlikely.
Evidence
- A1 Group — Investor Relations / Share Page other 3. September 2026
Official A1 Group investor relations page showing shareholder structure: América Móvil (~56-58%) and ÖBAG (~28%), with ISIN AT0000720008 listed on Vienna Stock Exchange.
Relevance: Confirms majority control by América Móvil (private, non-sovereign Mexican entity) and significant Austrian state stake via ÖBAG, establishing current ownership stability. - América Móvil and ÖBAG extend partnership (ÖBAG Newsroom, Feb 2023) other 3. September 2026
Official ÖBAG announcement of 10-year extension of syndicate agreement with América Móvil, securing Vienna HQ, stock exchange listing, and ÖBAG supervisory board nominations.
Relevance: Demonstrates long-term stability of ownership structure and Austrian state's continued engagement through 2033, reducing change-of-control risk. - Telekom Austria AG Results Report 2024 other 3. September 2026
Official 2024 financial report detailing ÖBAG's veto rights on capital increases, headquarters relocation, auditor appointment, and related party transactions under the Austria Package.
Relevance: Documents the Austria Package governance protections that prevent change of control without ÖBAG consent, including blocking minority rights and 75% supermajority thresholds.
All possible answer options (5)
- 1. Very likely (value 0.00, SEAL 4)
- 2. Likely takeover by or transfer to a non-EU sovereign entity (value 31.00, SEAL 4)
- 3. Somewhat likely takeover by or transfer to a non-EU sovereign entity (value 62.00, SEAL 4)
- 4. Unlikely takeover by or transfer to a non-EU sovereign entity (value 93.00, SEAL 4)
- 5. Very unlikely (value 125.00, SEAL 4) ✓
Selected answer: 3. Governance bodies exist with EU actors participation Value 83 SEAL 3
Notes: ÖBAG (Austrian state) holds SB chair and veto rights via syndicate agreement, but AMX (non-EU) controls majority stake and CEO nomination.
Evidence
- América Móvil and ÖBAG extend partnership (ÖBAG Newsroom, Feb 2023) other 3. September 2026
Official ÖBAG announcement of 10-year extension of syndicate agreement with América Móvil, securing Vienna HQ, stock exchange listing, and ÖBAG supervisory board nominations.
Relevance: Shows EU actor (ÖBAG) holds governance positions incl. SB chair and Deputy CEO in parent A1 Group, but lacks full control as América Móvil dominates strategic direction. - Corporate Governance — A1 Group other 3. September 2026
A1 Group corporate governance page detailing Management Board, Supervisory Board, and syndicate agreement governing co-operation between América Móvil and ÖBAG.
Relevance: Confirms formal governance bodies exist where EU actors (ÖBAG) participate through supervisory board seats and nomination rights per the syndicate agreement. - Telekom Austria AG Results Report 2024 other 3. September 2026
Official 2024 financial report detailing ÖBAG veto rights on capital increases, HQ relocation, auditor appointment, and related party transactions.
Relevance: Evidences EU actor's (ÖBAG) concrete veto powers on strategic corporate decisions, influencing but not fully controlling the parent group's roadmap direction.
All possible answer options (4)
- 1. No influence possible (value 0.00, SEAL 2)
- 2. Through "voice of the customer" public channels (e.g. feedback portals, online communities) (value 41.00, SEAL 2)
- 3. Governance bodies exist with EU actors participation (value 83.00, SEAL 3) ✓
- 4. Full influence of EU actors (value 125.00, SEAL 4)
Selected answer: 2. Mostly relying on non-EU funding Value 31 SEAL 4
Notes: A1 Group (Exoscale's ultimate parent) is majority-owned (~56-58%) by América Móvil (Mexico). EU state stake (ÖBAG) is ~28%. Majority non-EU capital.
Evidence
- A1 Group — Investor Relations / Share Page other 3. September 2026
Official A1 Group investor relations page showing shareholder structure: América Móvil (~56-58%) and ÖBAG (~28%), with ISIN AT0000720008 listed on Vienna Stock Exchange.
Relevance: Directly shows majority ownership (~56-58%) by América Móvil (Mexico, non-EU), confirming majority reliance on non-EU capital for Exoscale's parent group. - A1 Telekom Austria Group — Wikipedia other 3. September 2026
Wikipedia article detailing América Móvil's ~58% majority stake in Telekom Austria and the 2014 syndicate agreement giving it controlling influence.
Relevance: Provides overview of the syndicate agreement and América Móvil's controlling majority stake, illustrating the non-EU capital dominance in Exoscale's parent organization. - América Móvil and ÖBAG extend partnership (ÖBAG Newsroom, Feb 2023) other 3. September 2026
Official ÖBAG announcement of 10-year extension of syndicate agreement with América Móvil, securing Vienna HQ, stock exchange listing, and ÖBAG supervisory board nominations.
Relevance: Confirms ÖBAG (Austrian state, EU) holds ~28% stake with veto rights, but as minority shareholder limited EU capital influence compared to non-EU majority owner.
All possible answer options (5)
- 1. Almost entirely relying on non-EU funding (value 0.00, SEAL 4)
- 2. Mostly relying on non-EU funding (value 31.00, SEAL 4) ✓
- 3. Balanced mix of EU and non-EU funding (value 62.00, SEAL 4)
- 4. Majority of funding is EU-based (value 93.00, SEAL 4)
- 5. Entirely EU-based funding (value 125.00, SEAL 4)
Selected answer: 3. Balanced EU/non-EU Value 62 SEAL 4
Notes: Exoscale is HQ in Switzerland (non-EU/EEA). Parent A1 Digital (Vienna) invests in EU: €40M Vienna DC, expansion to Spain, DCs in DE/AT/BG/HR/CZ. A1 Group has €5.4B revenue, ~17k employees in EU.
Evidence
- A1 & Exoscale Open Second Public Cloud Zone in Vienna other 3. September 2026
Press release on €40M A1 datacenter investment in Vienna, Tier III facility with 2,550m² white space, connected load 12MW.
Relevance: Quantifies concrete EU investment by A1 Digital/Exoscale — €40M Vienna data center, demonstrating significant capital deployment in the EU. - A1 Group Corporate Presentation 2025 other 3. September 2026
A1 Group FY2024: €5.4B revenue, €2B EBITDA, 17,298 employees across 7 European markets. A1 Digital operates in Germany and Switzerland.
Relevance: Provides scale of parent group's EU economic footprint — revenue, employees, and market presence across Central/Southeastern Europe. - Exoscale Data Centers other 3. September 2026
Lists 8 European cloud zones: 2 Germany, 2 Austria, 2 Switzerland, 1 Bulgaria, 1 Croatia. All GDPR-compliant, 100% renewable energy.
Relevance: Shows Exoscale's European infrastructure footprint and investment across multiple EU/EEA countries, directly relevant to EU economic contribution assessment.
All possible answer options (5)
- 1. Minimal (value 0.00, SEAL 4)
- 2. Some (value 31.00, SEAL 4)
- 3. Balanced EU/non-EU (value 62.00, SEAL 4) ✓
- 4. Majority in the EU (value 93.00, SEAL 4)
- 5. Fully in the EU (value 125.00, SEAL 4)
Selected answer: 2. Active participant in strategic projects Value 62 SEAL 4
Notes: Exoscale is a Day One Member and Silver Market-X Partner of Gaia-X, confirming active participation in a key EU strategic initiative. No evidence of IPCEI-CIS or Horizon Europe involvement.
Evidence
- GAIA-X Cloud Initiative from Europe for Europe — Exoscale Blog other 3. September 2026
Exoscale blog announcing Day One Membership in Gaia-X through A1 Group, with participation in working groups contributing security and architecture expertise.
Relevance: Directly confirms Exoscale as a Day One Member of Gaia-X, one of the EU strategic programs listed in the assessment question, with active contributions to working groups. - Gaia-X Market-X Partners — Official Gaia-X Website other 3. September 2026
Official Gaia-X partners page listing Exoscale as a Silver-tier Market-X Partner alongside Aruba.it, deltaDAO, WOBCOM, and others.
Relevance: Official recognition of Exoscale as a Silver Market-X Partner confirms formal, ongoing participation in the Gaia-X strategic initiative at an institutional level. - STL Partners — What does IPCEI CIS tell us about the future of edge and cloud in Europe? other 3. September 2026
Analytical overview of IPCEI-CIS listing 19 direct participants including Orange, SAP, Telefonica, IONOS — but not Exoscale or A1 Digital.
Relevance: Provides context that Exoscale is not a named participant in IPCEI-CIS, narrowing their strategic program participation primarily to Gaia-X.
All possible answer options (3)
- 1. No clear participation (value 0.00, SEAL 4)
- 2. Active participant in strategic projects (value 62.00, SEAL 4) ✓
- 3. Strategic projects depend on contractor's involvement (value 125.00, SEAL 4)
Selected answer: Existing Action plan (how to measure ambition? Through means linked to the goals? Relative to the size of the company?) Value 41 SEAL 4
Notes: Exoscale aligns with EU digital (Gaia-X/Structura-X) and green (100% renewables) strategies with measurable actions, but ambition is moderate relative to size and lacks IPCEI-CIS participation.
Evidence
- A1 Telekom Austria Group Joins Structura-X other 3. September 2026
A1 Group joins Structura-X, a Gaia-X infrastructure initiative, with Exoscale as GDPR-compliant cloud supporting European digital sovereignty.
Relevance: Shows continued alignment with EU industrial cloud strategy via Structura-X participation, expanding Exoscale's European infrastructure footprint. - GAIA-X Cloud Initiative from Europe for Europe — Exoscale Blog other 3. September 2026
Exoscale blog announcing Day One Membership in Gaia-X through A1 Group, with participation in working groups contributing security and architecture expertise.
Relevance: Shows alignment with EU digital sovereignty strategy through early Gaia-X membership and active working-group participation, though not at IPCEI-CIS level. - Sustainability | Exoscale other 3. September 2026
Details Exoscale's green strategy: 100% renewable energy in DE/CH/AT, carbon neutrality target 2030, ISO-compliant life cycle assessments, CSRD reporting.
Relevance: Demonstrates measurable alignment with EU green/digital strategy through renewable energy progress, LCA, and carbon neutrality targets tied to A1 Group ESG.
All possible answer options (3)
- Existing Action plan (how to measure ambition? Through means linked to the goals? Relative to the size of the company?) (value 41.00, SEAL 4) ✓
- Already measured achievement and existing dedicated governance (value 83.00, SEAL 4)
- Bold ambition and dedicated means (value 125.00, SEAL 4)
Selected answer: 4. Ability to source alternative suppliers or internalise key functions Value 93 SEAL 2
Notes: Built on open-source Apache CloudStack; open standards (S3, K8s) and data portability tools enable migration to alternative providers or self-hosting if support is withdrawn.
Evidence
- A Deep Dive into Exoscale SKS Internals other 3. September 2026
Technical blog revealing Exoscale's infrastructure is built on Apache CloudStack, an open-source IaaS platform, with Kubernetes, etcd, and cloud-init as core components.
Relevance: Confirms Exoscale's platform is based on open-source CloudStack, meaning the foundational technology can be self-hosted or sourced from alternative CloudStack providers if Exoscale withdraws support. - Apache CloudStack — Official Website other 3. September 2026
Official Apache CloudStack site describing it as an open-source IaaS cloud computing platform used by MSPs, telcos, and cloud providers with multi-hypervisor support and AWS API compatibility.
Relevance: Establishes that CloudStack is a mature, community-backed open-source platform, meaning customers relying on Exoscale could internalize or migrate to other CloudStack-based providers for continuity. - Exoscale Data Portability other 3. September 2026
Exoscale's data portability page detailing export methods using standard formats (QCOW2, S3-compatible, DB dumps), 30-day post-termination data availability, no switching fees, and EU Data Act compliance.
Relevance: Demonstrates concrete measures enabling customers to migrate workloads to alternative providers if Exoscale support is withdrawn, supporting option 4. Shows open formats and financial incentives for portability.
All possible answer options (4)
- 2. Service would likely stop but with a delay to provide time for customer reaction (value 31.00, SEAL 0)
- 3. Can continue temporarily based on contractual agreement with EC (value 62.00, SEAL 2)
- 4. Ability to source alternative suppliers or internalise key functions (value 93.00, SEAL 2) ✓
- 5. Full autonomy and continuity (value 125.00, SEAL 4)
SOV-2 — Legal & Jurisdictional Sovereignty
Legal & Jurisdictional sovereignty evaluates the legal environment, exposure to foreign authority, and enforceability of rights that govern a technology provider and its services. It determines the extent to which a provider is anchored in European jurisdiction and insulated from external legal claims.
Weight 10%
Selected answer: 2. Mixed EU/non-EU Value 84 SEAL 1
Notes: Ops entity is Swiss (non-EU); parent A1 Digital is Austrian (EU); majority owner América Móvil is Mexican (non-EU). Mixed EU/non-EU.
Evidence
- A1 Group — Investor Relations / Share Page other 3. September 2026
Official A1 Group investor relations page showing shareholder structure: América Móvil (~56-58%) and ÖBAG (~28%), with ISIN AT0000720008 listed on Vienna Stock Exchange.
Relevance: Proves ultimate majority ownership by Mexican (non-EU) company alongside Austrian (EU) state — combines with Swiss ops for mixed assessment. - About Us | Exoscale European Cloud Services other 3. September 2026
Official Exoscale page confirming Akenes SA (Switzerland) is the legal entity, part of A1 Digital and A1 Telekom Austria Group.
Relevance: Establishes Swiss (non-EU) operating entity under Austrian (EU) parent — core evidence of mixed EU/non-EU jurisdiction. - Terms and Conditions | Exoscale other 3. September 2026
Exoscale T&C naming Akenes SA (Lausanne, CH) as supplier; Swiss law governs with exclusive Vaud court jurisdiction.
Relevance: Directly proves contracts are governed by Swiss (non-EU) law, confirming non-EU legal jurisdiction for operations.
All possible answer options (3)
- 1. Non-EU only (value 0.00, SEAL 1)
- 2. Mixed EU/non-EU (value 84.00, SEAL 1) ✓
- 3. Exclusively EU law (value 167.00, SEAL 4)
Selected answer: EU subsidiary with contractual protections Value 83 SEAL 1
Notes: EU parent (A1 Digital, AT) with syndicate agreement & Swiss law T&Cs, but America Movil majority ownership leaves residual non-EU exposure.
Evidence
- A1 Digital European Cloud other 3. September 2026
A1 Digital product page for Exoscale claiming 100% European cloud, data centers in EU, and exemption from US CLOUD Act.
Relevance: Provider's own claim of CLOUD Act exemption and European sovereignty, key to assessing extraterritorial law exposure posture and degree of self-assessed insulation. - América Móvil and ÖBAG extend partnership (ÖBAG Newsroom, Feb 2023) other 3. September 2026
Official ÖBAG announcement of 10-year extension of syndicate agreement with América Móvil, securing Vienna HQ, stock exchange listing, and ÖBAG supervisory board nominations.
Relevance: Shows contractual protections (ÖBAG veto rights) shielding A1 Group from full non-EU control, but does not eliminate America Movil majority ownership exposure. - Terms and Conditions | Exoscale other 3. September 2026
Exoscale T&C naming Akenes SA (Lausanne, CH) as supplier; Swiss law governs with exclusive Vaud court jurisdiction.
Relevance: Establishes Swiss/Schengen legal jurisdiction for Exoscale operations, grounding the provider in European law and limiting exposure to non-EU legal authority.
All possible answer options (4)
- Mitigation clauses, exposure remains (value 41.00, SEAL 1)
- EU subsidiary with contractual protections (value 83.00, SEAL 1) ✓
- Legal structures shielding from foreign law (value 125.00, SEAL 2)
- Verified legal immunity, non-EU laws unenforceable (value 167.00, SEAL 4)
Selected answer: 4. Non-EU authorities requests to access data or systems are disputed by the provider and eventually in some cases are accepted with customers being notified Value 125 SEAL 1
Notes: Swiss-incorporated Exoscale blocks direct foreign data requests via Art. 271 SCC. Some accepted via Swiss mutual legal assistance with customer notification.
Evidence
- CLOUD Act vs GDPR: The Conflict About Data Access Explained — Exoscale Blog other 3. September 2026
Exoscale's analysis of the US CLOUD Act's extraterritorial reach and GDPR Article 48 conflict; confirms Exoscale, as a Swiss/European entity, is not subject to the CLOUD Act.
Relevance: Confirms Exoscale is not subject to US CLOUD Act; non-EU authorities cannot directly compel access. Direct foreign requests would be disputed under Swiss law. - GDPR Compliance — Exoscale other 3. September 2026
Exoscale's official GDPR compliance page confirming its Swiss incorporation, jurisdiction, and that as a European entity with no US parent it is not subject to the CLOUD Act.
Relevance: Confirms the provider's formal position that non-EU authority access must proceed via Swiss legal channels, not direct compulsion. Disputed случаев accepted only via Swiss process. - Managing Swiss Data Protection and Secrecy Laws in Cross-Border Investigations — Bär & Karrer other 3. September 2026
Swiss law firm analysis of Swiss blocking statutes (Art. 271, 273 SCC), which prohibit direct disclosure of data to foreign authorities without Swiss legal process involvement.
Relevance: Shows Swiss law requires foreign authority requests to go through mutual legal assistance channels. Some cases eventually accepted with procedural customer notification rights.
All possible answer options (4)
- 2. Non-EU authorities can compel access to data or systems without customers being notified, in specific cases (value 41.00, SEAL 1)
- 3. Non-EU authorities can compel access to data or systems with customers being notified in all cases (value 83.00, SEAL 1)
- 4. Non-EU authorities requests to access data or systems are disputed by the provider and eventually in some cases are accepted with customers being notified (value 125.00, SEAL 1) ✓
- 5. Non-EU authorities requests to access data or systems are always rejected by the provider (value 167.00, SEAL 4)
Selected answer: Part of the offer cannot be exposed to restrictions towards EU MSs or international organisations Value 167 SEAL 4
Notes: Exoscale's EUC imposes EAR on NVIDIA GPUs only (part of offer); restrictions target D:1/D:4/D:5 countries & sanctioned parties, not EU MSs or intl orgs.
Evidence
- BIS Country Guidance – Bureau of Industry and Security other 3. September 2026
BIS official guidance on export control country group designations and how countries are classified for licence exception eligibility under EAR Part 740.
Relevance: Authoritative U.S. government source explaining Country Group D designations restricted from certain exports; confirms EU MSs are in Groups A/B, not D, supporting that EAR restrictions do not target EU MSs or international organisations. - Exoscale End-User Certificate (EUC) for NVIDIA GPU Access other 3. September 2026
Exoscale's official EUC page outlining U.S. EAR compliance for controlled NVIDIA GPU instances (e.g., B300, RTX Pro 6000 Blackwell).
Relevance: Directly shows EAR restrictions apply only to GPU part of Exoscale offer; restrictions target Country Groups D:1/D:4/D:5, sanctioned parties, and military/WMD end-uses—not EU MSs or international organisations. - Supplement No. 1 to Part 740 – EAR Country Groups (eCFR) other 3. September 2026
Official eCFR text of EAR Country Groups A, B, D, and E, listing which countries fall into each restricted subgroup.
Relevance: Confirms no EU member states appear in Country Groups D:1 (National Security) or D:4 (Missile Technology); only Cyprus appears in D:5 (U.S. Arms Embargoed). EU MSs are generally not subject to EAR restrictions Exoscale's EUC targets.
All possible answer options (4)
- Restrictions exists towards EU citizens or international organisations (value 41.00, SEAL 1)
- Share of revenues >50% in the EU (value 83.00, SEAL 2)
- Part of the offer cannot be exposed to restrictions towards EU MSs (value 125.00, SEAL 3)
- Part of the offer cannot be exposed to restrictions towards EU MSs or international organisations (value 167.00, SEAL 4) ✓
Selected answer: 3. Mixed within/outside the EU Value 83 SEAL 4
Notes: IP created and registered in Switzerland (non-EU); development now spans EU (AT, DE, BG, HR) and non-EU (CH) locations.
Evidence
- A1 Digital Acquires Swiss Cloud Provider Exoscale other 3. September 2026
Swisscom Ventures article on A1 Digital's 2017 acquisition of Exoscale, expanding from Swiss base to EU access points.
Relevance: Confirms IP originated in Switzerland (non-EU) with subsequent expansion of development into EU countries via A1 Digital. - A1 Digital European Cloud other 3. September 2026
A1 Digital product page for Exoscale claiming 100% European cloud, data centers in EU, and exemption from US CLOUD Act.
Relevance: Shows dual jurisdiction: IP in Switzerland (non-EU) and parent org A1 Digital in Austria (EU), indicating mixed IP location. - About Us | Exoscale European Cloud Services other 3. September 2026
Official Exoscale page confirming Akenes SA (Switzerland) is the legal entity, part of A1 Digital and A1 Telekom Austria Group.
Relevance: Confirms IP creation and registration origin in Switzerland (non-EU), with European development team based there.
All possible answer options (4)
- 2. Mostly outside the EU (value 41.00, SEAL 4)
- 3. Mixed within/outside the EU (value 83.00, SEAL 4) ✓
- 4. Mostly within the EU (value 125.00, SEAL 4)
- 5. Fully within the EU (value 167.00, SEAL 4)
Selected answer: Mixed law, some EU Value 83 SEAL 3
Notes: IP owned by Akenes SA (Switzerland, non-EU) under Swiss law; parent A1 Digital (Austria, EU); majority shareholder América Móvil (Mexico, non-EU). Mixed jurisdictions with some EU presence.
Evidence
- A1 Telekom Austria Group — Wikipedia other 3. September 2026
Wikipedia article detailing América Móvil's ~58% majority stake in Telekom Austria and the 2014 syndicate agreement giving it controlling influence.
Relevance: Shows the corporate ownership chain: IP holder Akenes SA (Swiss/non-EU) → A1 Digital (Austria/EU) → América Móvil (Mexico/non-EU), confirming mixed jurisdictional structure. - About Us | Exoscale European Cloud Services other 3. September 2026
Official Exoscale page confirming Akenes SA (Switzerland) is the legal entity, part of A1 Digital and A1 Telekom Austria Group.
Relevance: Establishes IP ownership chain: Exoscale trademarks held in Switzerland (non-EU) by Akenes SA, with parent group in Austria (EU) and ultimate majority owner América Móvil (Mexico, non-EU). - End User Service Agreement (EUSA) | Exoscale other 3. September 2026
Exoscale's EUSA confirms IP ownership: clients retain rights to their technology/data; Exoscale retains rights to its platform. Governed by Swiss law, exclusive jurisdiction courts of Vaud, Lausanne.
Relevance: Directly shows IP rights are owned by Akenes SA (Swiss entity) and enforced under Swiss (non-EU) law, confirming IP holder jurisdiction is primarily non-EU.
All possible answer options (4)
- non-EU law, mixed non-EU countries (value 41.00, SEAL 3)
- Mixed law, some EU (value 83.00, SEAL 3) ✓
- EU law with exceptions (value 125.00, SEAL 4)
- fully under EU law (value 167.00, SEAL 4)
SOV-3 — Data & AI Sovereignty
Data & AI sovereignty focuses on the protection, control, and independence of data assets and AI services within the EU/EEA. It addresses how data is secured, where it is processed, and the degree of autonomy customers retain over AI capabilities.
Weight 10%
Selected answer: 4. Customer primary control but provider can read the data or some of the data Value 150 SEAL 3
Notes: Exoscale offers CYOK via KMS — customers control key lifecycle, but keys reside in Exoscale's boundary. Root key is provider-managed. HYOK/XKS only planned.
Evidence
- Encryption at Rest & In Transit | Exoscale other 3. September 2026
Official Exoscale page detailing encryption at rest (AES-256-XTS), encryption in transit (TLS), and the CYOK key management model via KMS.
Relevance: Shows customers control key lifecycle (create, rotate, disable, delete) but keys are stored within Exoscale's cryptographic boundary. HYOK/XKS is only planned, not available. Root key is provider-managed. - Exoscale Key Management Service (KMS) is Now Available other 3. September 2026
Announcement of KMS general availability as a standalone service with lifecycle control, rotation, deletion, and audit trails.
Relevance: Confirms KMS is available as standalone service but notes integration with storage/compute resources is still pending, limiting current customer key control over actual data encryption. - Exoscale KMS — Overview (Technical Documentation) other 3. September 2026
Technical documentation for Exoscale KMS detailing key hierarchy, envelope encryption, and cryptographic primitives (AES-256-GCM, HKDF).
Relevance: Reveals the key hierarchy where the Root Key is Exoscale-managed, meaning the provider controls the top of the key chain. KMS keys (customer-controlled) sit below the provider-managed root.
All possible answer options (4)
- 2. Primarily the provider but not exclusively (value 50.00, SEAL 1)
- 3. Shared - provider has override keys (value 100.00, SEAL 2)
- 4. Customer primary control but provider can read the data or some of the data (value 150.00, SEAL 3) ✓
- 5. Customer exclusive control - provider can not read the data (value 200.00, SEAL 4)
Selected answer: 4. Full customer controlled visibility of log access but not in real time Value 150 SEAL 3
Notes: Audit Trail logs who/what/when/where with customer-controlled SOS bucket storage. SOC 2 assures auditability, but platform logs are not real-time.
Evidence
- Audit Trail — Exoscale Community Documentation other 3. September 2026
Exoscale's Audit Trail tracks all security-relevant user activity and API usage. Events include origin, owner, and resource details. Short-term retention 30 days; long-term stored in customer's own SOS bucket (daily uploads, 2-hour event windows).
Relevance: Demonstrates customer-controlled log visibility by storing long-term audit events in the customer's own SOS bucket. Captures who, what, when, and where. But updates are batched (2-hour windows), not real-time. - Kubernetes Audit Log Available on Exoscale SKS — Exoscale Blog other 3. September 2026
Exoscale SKS supports forwarding Kubernetes API Server audit logs to a customer-configured webhook endpoint, enabling real-time security analysis with tools like Falco. Full customer control over audit data destination.
Relevance: Shows real-time, customer-controlled audit logging for Kubernetes workloads (including AI/model workloads deployed on SKS), but this is limited to SKS clusters, not the broader platform. - SOC 2 Compliance | Exoscale other 3. September 2026
Exoscale holds a SOC 2 Type 2 report (available since 2023) verified by an independent CPA firm, covering Security, Availability, Processing Integrity, Confidentiality, and Privacy controls.
Relevance: Independent SOC 2 Type 2 audit provides third-party assurance of access logging and governance controls, supporting the independent auditability dimension of the assessment question.
All possible answer options (4)
- 2. Basic logs incomplete (missing date; missing user; missing type of access; missing means of access etc.) (value 50.00, SEAL 1)
- 3. Logs exist but not real-time or controlled by vendor (vendor is replaced by CUSTOMER in the survey) (value 100.00, SEAL 2)
- 4. Full customer controlled visibility of log access but not in real time (value 150.00, SEAL 3) ✓
- 5. Real-time customer oversight and independent auditability (value 200.00, SEAL 4)
Selected answer: 3. Internal validation based on policies - no proof of validation left Value 100 SEAL 1
Notes: EUSA mandates erasure and confirms completion upon request, but no systematic proof or independent verification of erasure is provided.
Evidence
- Cloud Security | How Exoscale Keeps Your Data Safe other 3. September 2026
Exoscale security page detailing ISO 27001-certified datacenters, drive decommissioning, and Swiss data protection laws.
Relevance: Mentions drive destruction or cryptographic locking for decommissioned drives, but no systematic verification mechanism for customer data erasure with proof. - End User Service Agreement (EUSA) | Exoscale other 3. September 2026
Exoscale's EUSA confirms IP ownership: clients retain rights to their technology/data; Exoscale retains rights to its platform. Governed by Swiss law, exclusive jurisdiction courts of Vaud, Lausanne.
Relevance: Contractually mandates data erasure and offers confirmation upon request, but does not provide systematic proof or independent verification of irreversible deletion. - GDPR Compliance — Exoscale other 3. September 2026
Exoscale's official GDPR compliance page confirming its Swiss incorporation, jurisdiction, and that as a European entity with no US parent it is not subject to the CLOUD Act.
Relevance: Confirms GDPR right-to-erasure compliance but provides no technical details on how deletion is verified or proof of erasure is delivered.
All possible answer options (4)
- 2. Manual confirmation only (value 50.00, SEAL 1)
- 3. Internal validation based on policies - no proof of validation left (value 100.00, SEAL 1) ✓
- 4. Deletion is technically verified with access logs (value 150.00, SEAL 3)
- 5. Yes, irreversible deletion is systematically enforced and independently verified (value 200.00, SEAL 4)
Selected answer: 4. Data in the EU by default, tightly controlled exceptions Value 150 SEAL 1
Notes: 6 of 8 zones in EU; 2 in Switzerland (non-EU/EEA but with adequacy decision). All data in Europe, no non-European fallback, no CLOUD Act exposure.
Evidence
- Exoscale Data Centers other 3. September 2026
Lists 8 European cloud zones: 2 Germany, 2 Austria, 2 Switzerland, 1 Bulgaria, 1 Croatia. All GDPR-compliant, 100% renewable energy.
Relevance: Shows all data centers are in Europe with 6 in EU member states and 2 in Switzerland (non-EU/EEA), confirming data is mainly in EU with tightly controlled Swiss exception. - Exoscale Zone Documentation other 3. September 2026
Technical documentation detailing Exoscale's zone concept: 8 geographically isolated zones in Vienna, Sofia, Zurich, Geneva, Frankfurt, Munich, and Zagreb, all independently operated.
Relevance: Confirms zone architecture and that resources are zone-specific with no cross-border data movement, reinforcing EU-confinement with Swiss exception. - Sovereign Cloud and Data Sovereignty: An Overview — Exoscale Blog other 3. September 2026
Detailed blog post explaining EU Cloud Sovereignty Framework, distinction between data sovereignty and data residency, and why US hyperscalers cannot guarantee EU sovereignty due to CLOUD Act.
Relevance: Explains Exoscale's sovereignty positioning, confirming European jurisdiction with no third-country fallback and no CLOUD Act exposure, supporting the assessment.
All possible answer options (4)
- 2. Data partly in the EU, significant reliance on third countries and limited control (value 50.00, SEAL 0)
- 3. Data mainly in the EU, some third-country use with standard safeguards (value 100.00, SEAL 1)
- 4. Data in the EU by default, tightly controlled exceptions (value 150.00, SEAL 1) ✓
- 5. All data exclusively in the EU with no third-country fallback (value 200.00, SEAL 4)
Selected answer: Mixed Control with alternatives: Auditable or open source AI, foreign chips Value 100 SEAL 2
Notes: EU-hosted AI infra supports open-source models (Hugging Face), but relies entirely on NVIDIA GPUs/chips. No EU-origin AI models or domestic chip alternatives.
Evidence
- Exoscale AI Cloud Infrastructure other 3. September 2026
Exoscale AI suite: NVIDIA GPU instances, managed/dedicated inference for open-source Hugging Face models, vector databases — all hosted in European data centers.
Relevance: Shows AI services run on European infra with auditable open-source models, but no EU-origin AI development. Complete NVIDIA chip dependency for compute. - Exoscale GPU Cloud Servers other 3. September 2026
GPU instances using NVIDIA B300, RTX Pro 6000 Blackwell, A40, A30, A5000, Tesla V100, RTX 3080 Ti. NGC integration, TensorFlow/PyTorch support out of the box.
Relevance: Confirms total dependency on foreign (US) NVIDIA chips and CUDA ecosystem. No European accelerator alternatives offered for AI workloads. - The E.U.'s AI Drive Undermines Its Own Chip Strategy other 2. September 2026
IEEE Spectrum article on EU semiconductor dependency, noting Europe produces under 10% of global chips and relies heavily on US designers and Asian manufacturers.
Relevance: Contextualizes Exoscale's NVIDIA dependency as a systemic Europe-wide challenge, not provider-specific; no EU AI chip alternatives available at scale today.
All possible answer options (4)
- Mostly non-EU dependencies: Licensed AI, chip dependency (value 50.00, SEAL 2)
- Mixed Control with alternatives: Auditable or open source AI, foreign chips (value 100.00, SEAL 2) ✓
- EU-led AI, foreign accelerators (value 150.00, SEAL 3)
- EU-origin models and chips - no dependencies from outside EU (value 200.00, SEAL 4)
SOV-4 — Operational Sovereignty
Operational sovereignty measures the practical ability of EU actors to run, support, and evolve a technology independently of foreign control. It focuses on continuity of operations, skill availability, and resilience against external dependencies.
Weight 15%
Selected answer: 3. Standard documented methods for data export are available Value 83 SEAL 4
Notes: Exoscale provides documented data export via QCOW2, S3 API, and DB dumps with migration guides, EU Data Act compliance, and no switching fees — but no formal migration service offering.
Evidence
- Apache CloudStack — Official Website other 3. September 2026
Official Apache CloudStack site describing it as an open-source IaaS cloud computing platform used by MSPs, telcos, and cloud providers with multi-hypervisor support and AWS API compatibility.
Relevance: Exoscale is built on Apache CloudStack, an open-source platform with AWS API compatibility, reducing lock-in and easing interoperability with alternative EU solutions. - Exoscale Data Portability other 3. September 2026
Exoscale's data portability page detailing export methods using standard formats (QCOW2, S3-compatible, DB dumps), 30-day post-termination data availability, no switching fees, and EU Data Act compliance.
Relevance: Direct evidence that standard documented export methods are available for all data types, with migration guidance, 30-day post-termination data availability, and waived egress fees. - From AWS to Exoscale: A Report on Experiences other 3. September 2026
Real-world case study of migrating from AWS to Exoscale: service mapping, zero-downtime DB migration via replication, S3 sync with rclone, IaC rebuild with Pulumi.
Relevance: Shows migration relies on standard tooling (rclone, logical replication, Pulumi) rather than dedicated migration services, confirming option 3 over option 4.
All possible answer options (4)
- 2. Data export and workload portability is provided on a "best-effort" basis (value 41.00, SEAL 1)
- 3. Standard documented methods for data export are available (value 83.00, SEAL 4) ✓
- 4. Formal migration services are available to assist with moving data and workloads (value 125.00, SEAL 4)
- 5. Solution already deployed on sovereign infrastructure (value 167.00, SEAL 4)
Selected answer: 4. Operational services are predominantly delivered by EU-based teams Value 125 SEAL 3
Notes: EU-based engineering and support teams manage all operations; however NVIDIA GPU dependencies and non-EU majority shareholder create partial foreign dependencies.
Evidence
- About Us | Exoscale European Cloud Services other 3. September 2026
Official Exoscale page confirming Akenes SA (Switzerland) is the legal entity, part of A1 Digital and A1 Telekom Austria Group.
Relevance: Confirms leadership and operational team are EU-based; all engineering roles located in Europe. Demonstrates capacity for EU-based operational management. - Exoscale Jobs – Engineering Roles in Europe other 3. September 2026
Job listings for SREs, hardware engineers, and capacity planners based in Madrid, Munich, and Lausanne with EU remote option.
Relevance: Shows operational support roles (SRE, on-call, infrastructure) are exclusively EU-based, confirming EU capacity to run and maintain the platform independently. - Sovereign Cloud and Data Sovereignty: An Overview — Exoscale Blog other 3. September 2026
Detailed blog post explaining EU Cloud Sovereignty Framework, distinction between data sovereignty and data residency, and why US hyperscalers cannot guarantee EU sovereignty due to CLOUD Act.
Relevance: Directly addresses operational sovereignty criteria; confirms that Exoscale positions EU-based operations and support as core to its sovereign cloud offering.
All possible answer options (4)
- 2. Operational services are partially sourced from within the EU (value 41.00, SEAL 1)
- 3. Operational responsibilities are balanced between EU and non-EU teams (value 83.00, SEAL 3)
- 4. Operational services are predominantly delivered by EU-based teams (value 125.00, SEAL 3) ✓
- 5. The entire technology stack is managed and supported by a fully EU-based team (value 167.00, SEAL 4)
Selected answer: Majority EU, escalation abroad Value 83 SEAL 3
Notes: Staff primarily EU-based (AT, DE, ES, BG); HQ in Switzerland + A1 Group ops in Serbia/Belarus constitute non-EU escalation paths.
Evidence
- A1 Digital European Cloud other 3. September 2026
A1 Digital product page for Exoscale claiming 100% European cloud, data centers in EU, and exemption from US CLOUD Act.
Relevance: Confirms sovereign operational model and European-based support structure for sustaining the Exoscale service. - Exoscale Jobs – Engineering Roles in Europe other 3. September 2026
Job listings for SREs, hardware engineers, and capacity planners based in Madrid, Munich, and Lausanne with EU remote option.
Relevance: Shows operational and engineering staff distributed across EU member states with HQ in Switzerland. - Exoscale on Remote In Tech other 3. September 2026
Company profile showing ~85 employees, HQ in Lausanne, Vienna office, 100% EU remote work policy.
Relevance: Confirms predominantly EU-based operational team, identifies size and geographic distribution of staff.
All possible answer options (4)
- Mixed, majority outside EU (value 41.00, SEAL 1)
- Majority EU, escalation abroad (value 83.00, SEAL 3) ✓
- All EU staff (value 125.00, SEAL 3)
- 100% EU staff + clearance (value 167.00, SEAL 4)
Selected answer: 3. The majority of support staff are in the EU but escalations are handled by non-EU teams Value 83 SEAL 3
Notes: Most SRE/support staff in EU (Vienna, Munich, Madrid, remote-EU); HQ in Lausanne, CH (non-EU/EEA) likely handles escalations.
Evidence
- Exoscale Jobs – Engineering Roles in Europe other 3. September 2026
Job listings for SREs, hardware engineers, and capacity planners based in Madrid, Munich, and Lausanne with EU remote option.
Relevance: Shows SRE roles (who handle on-call support) are based in EU (Madrid, Munich) while hardware/capacity roles are in Lausanne, CH (non-EU/EEA). - Exoscale on Remote In Tech other 3. September 2026
Company profile showing ~85 employees, HQ in Lausanne, Vienna office, 100% EU remote work policy.
Relevance: Confirms ~85 employees with HQ in Switzerland (non-EU/EEA) and an EU office in Vienna. Suggests senior/escalation roles may be aligned to Swiss HQ. - Support Plans | Exoscale other 3. September 2026
Details Exoscale's four support tiers (Built-In to Enterprise), support hours in CET/CEST, and confirms support is handled by in-house engineers, not outsourced.
Relevance: Confirms support is delivered by internal staff during EU business hours (CET), with Enterprise tier offering 24/7. No mention of non-EU support teams.
All possible answer options (4)
- 2. The team is mixed but the majority of support staff reside outside the EU (value 41.00, SEAL 2)
- 3. The majority of support staff are in the EU but escalations are handled by non-EU teams (value 83.00, SEAL 3) ✓
- 4. All support staff are located within the EU (value 125.00, SEAL 3)
- 5. All support staff are located within the EU and hold relevant security clearances (value 167.00, SEAL 4)
Selected answer: 4. EU-only primary repositories - All primary documentation and knowledge repositories are stored in the EU (no routine non-EU storage/processing) Value 125 SEAL 4
Notes: All documentation hosted on EU infrastructure; open-source tools & SDKs publicly available; operational know-how with EU-based engineering team.
Evidence
- Exoscale GitHub Organization — Open-Source Repositories other 3. September 2026
299 public repositories including CLI (exo), Terraform provider, Go SDK (egoscale), Python SDK, Kubernetes CSI driver, Karpenter provider, and Cloud Controller Manager.
Relevance: Shows source code availability through open-source repositories. Tools are publicly available, though hosted on GitHub (US-based). Core platform relies on Apache CloudStack (open-source). - Exoscale Reference Hub — API, CLI, Terraform, SDKs other 3. September 2026
Central documentation hub covering full API reference, exo CLI, IAM, Terraform provider, Crossplane providers, and language SDKs (Go, Python).
Relevance: Demonstrates comprehensive technical documentation availability hosted on Exoscale's EU-based community site, enabling long-term operational autonomy for EU actors. - Support Plans | Exoscale other 3. September 2026
Details Exoscale's four support tiers (Built-In to Enterprise), support hours in CET/CEST, and confirms support is handled by in-house engineers, not outsourced.
Relevance: Demonstrates operational know-how is retained within EU-based engineering team, supporting long-term autonomy without dependence on non-EU support staff.
All possible answer options (4)
- 2. EU optional, not enforced - EU storage is available as an option, but it is not enforced (value 41.00, SEAL 2)
- 3. EU primary with non-EU fallback - Stored/managed in the EU by default, but some storage/replication/access outside the EU may occur (e.g., disaster recovery/support) (value 83.00, SEAL 4)
- 4. EU-only primary repositories - All primary documentation and knowledge repositories are stored in the EU (no routine non-EU storage/processing) (value 125.00, SEAL 4) ✓
- 5. EU-only end-to-end - Content, metadata, and backups/replicas are stored in the EU and privileged administration/support access is restricted to EU-based staff under EU jurisdiction (value 167.00, SEAL 4)
Selected answer: 4. Ability to source alternative suppliers or internalise key functions Value 125 SEAL 3
Notes: Core platform is open-source (Apache CloudStack), enabling internalisation. Backed by large EU telecom group (A1) for alternative sourcing, though non-EU majority ownership limits full autonomy.
Evidence
- A1 Digital European Cloud other 3. September 2026
A1 Digital product page for Exoscale claiming 100% European cloud, data centers in EU, and exemption from US CLOUD Act.
Relevance: Shows A1 Digital's European supplier network and infrastructure across multiple EU countries, providing ability to source alternative suppliers within the group. - A1 Telekom Austria Group — Wikipedia other 3. September 2026
Wikipedia article detailing América Móvil's ~58% majority stake in Telekom Austria and the 2014 syndicate agreement giving it controlling influence.
Relevance: Reveals ultimate ownership includes non-EU majority stakeholder (América Móvil), which limits full operational autonomy and affects supplier decision-making jurisdiction. - Apache CloudStack — Official Website other 3. September 2026
Official Apache CloudStack site describing it as an open-source IaaS cloud computing platform used by MSPs, telcos, and cloud providers with multi-hypervisor support and AWS API compatibility.
Relevance: Demonstrates Exoscale's core platform is open-source, meaning key software functions can be internalised rather than dependent on proprietary suppliers — critical for subcontractor independence.
All possible answer options (4)
- 2. Service would likely stop but with a delay to provide time for customer reaction (value 41.00, SEAL 2)
- 3. Can continue temporarily based on contractual agreement with EC (value 83.00, SEAL 3)
- 4. Ability to source alternative suppliers or internalise key functions (value 125.00, SEAL 3) ✓
- 5. Full autonomy and continuity (value 167.00, SEAL 4)
SOV-5 — Supply Chain Sovereignty
Supply chain sovereignty evaluates the geographic origin, transparency, and resilience of the technology supply chain, focusing on the extent to which critical components and processes remain under EU control or exposed to non-EU dependencies.
Weight 10%
Selected answer: Transparent with exceptions Value 71 SEAL 3
Notes: Partial disclosure: Exoscale names data center partners and GPU models but omits server, networking, storage OEMs and their geographic origin.
Evidence
- A1 Digital European Cloud other 3. September 2026
A1 Digital product page for Exoscale claiming 100% European cloud, data centers in EU, and exemption from US CLOUD Act.
Relevance: Confirms partial supplier disclosure: GPU supplier (NVIDIA, US-based) is named, but server, storage, and networking OEM vendors remain undisclosed. - Exoscale Data Centers other 3. September 2026
Lists 8 European cloud zones: 2 Germany, 2 Austria, 2 Switzerland, 1 Bulgaria, 1 Croatia. All GDPR-compliant, 100% renewable energy.
Relevance: Shows partial transparency: data center operators named, but server, networking, and storage hardware OEMs and their geographic origins are not disclosed. - Sovereign Cloud and Data Sovereignty: An Overview — Exoscale Blog other 3. September 2026
Detailed blog post explaining EU Cloud Sovereignty Framework, distinction between data sovereignty and data residency, and why US hyperscalers cannot guarantee EU sovereignty due to CLOUD Act.
Relevance: Exoscale explicitly acknowledges supply chain transparency questions but does not provide its own comprehensive disclosure of component origins or supplier provenance.
All possible answer options (4)
- Partial disclosure (value 35.00, SEAL 1)
- Transparent with exceptions (value 71.00, SEAL 3) ✓
- Full transparency (value 107.00, SEAL 3)
- EU-certified provenance (value 143.00, SEAL 4)
Selected answer: Build by EU Teams, on the basis of a foreign code Value 107 SEAL 3
Notes: EU hardware team in Lausanne designs/specifies servers, but core components (NVIDIA GPUs, x86 CPUs) are foreign-designed and manufactured outside EU.
Evidence
- Exoscale Data Centers other 3. September 2026
Lists 8 European cloud zones: 2 Germany, 2 Austria, 2 Switzerland, 1 Bulgaria, 1 Croatia. All GDPR-compliant, 100% renewable energy.
Relevance: Shows mixed facility sourcing — A1 (Austrian/EU) for some zones and Equinix (US) for others, with EU-based Diggers liquid cooling trial in Vienna. Existing evidence ID 504. - Exoscale GPU Cloud Servers other 3. September 2026
GPU instances using NVIDIA B300, RTX Pro 6000 Blackwell, A40, A30, A5000, Tesla V100, RTX 3080 Ti. NGC integration, TensorFlow/PyTorch support out of the box.
Relevance: Confirms GPU components are foreign-origin (NVIDIA fabless, TSMC Taiwan manufacturing), establishing non-EU dependency in hardware supply chain. Existing evidence ID 535. - Exoscale Jobs – Engineering Roles in Europe other 3. September 2026
Job listings for SREs, hardware engineers, and capacity planners based in Madrid, Munich, and Lausanne with EU remote option.
Relevance: Shows Exoscale has an EU-based hardware engineering team designing and specifying server infrastructure, but they build on foreign-designed components (NVIDIA, Intel/AMD). Existing evidence ID 537.
All possible answer options (4)
- Foreign origin, partial disclosure (value 35.00, SEAL 1)
- Mixed sourcing, EU audit rights (value 71.00, SEAL 3)
- Build by EU Teams, on the basis of a foreign code (value 107.00, SEAL 3) ✓
- Exclusive designed and build by EU Teams (value 143.00, SEAL 4)
Selected answer: Partial disclosure Value 35 SEAL 4
Notes: Open-source control stack (KVM, CloudStack) is auditable; GPU models (NVIDIA) disclosed. Firmware provenance, SBOMs, and server hardware suppliers undisclosed.
Evidence
- A Deep Dive into Exoscale SKS Internals other 3. September 2026
Details Exoscale's infrastructure stack built on Apache CloudStack, KVM virtualization, etcd, and cloud-init — all open-source components.
Relevance: Demonstrates software-layer transparency via open-source control stack, but does not cover embedded firmware or hardware component provenance, confirming partial disclosure on embedded code origin. - Apache CloudStack — Official Website other 3. September 2026
Official Apache CloudStack site describing it as an open-source IaaS cloud computing platform used by MSPs, telcos, and cloud providers with multi-hypervisor support and AWS API compatibility.
Relevance: Confirms the control plane software is open-source and auditable, providing provenance for the software layer controlling hardware, but not for firmware embedded in physical components. - Exoscale Data Centers other 3. September 2026
Lists 8 European cloud zones: 2 Germany, 2 Austria, 2 Switzerland, 1 Bulgaria, 1 Croatia. All GDPR-compliant, 100% renewable energy.
Relevance: Shows partial disclosure: facility partners and networking topology are public, but no hardware vendor names or firmware/component provenance is provided, directly relevant to embedded code origin assessment.
All possible answer options (4)
- Partial disclosure (value 35.00, SEAL 4) ✓
- Transparent with exceptions (value 71.00, SEAL 4)
- Full transparency (value 107.00, SEAL 4)
- EU-certified provenance (value 143.00, SEAL 4)
Selected answer: 3. Core and essential parts of the software are designed and maintained by EU teams Value 71 SEAL 3
Notes: Exoscale's platform is built on Apache CloudStack (US-origin) and other global FOSS, but core custom software is developed by EU-based teams in Lausanne, Vienna, Munich, and Madrid. Foreign-origin dependencies prevent higher maturity.
Evidence
- A Deep Dive into Exoscale SKS Internals other 3. September 2026
Technical blog revealing Exoscale's infrastructure is built on Apache CloudStack, an open-source IaaS platform, with Kubernetes, etcd, and cloud-init as core components.
Relevance: Directly shows software origin: foundation is US-origin CloudStack; Exoscale's EU team built the essential platform software on top. - Exoscale GitHub Organization — Open-Source Repositories other 3. September 2026
299 public repositories including CLI (exo), Terraform provider, Go SDK (egoscale), Python SDK, Kubernetes CSI driver, Karpenter provider, and Cloud Controller Manager.
Relevance: Shows the in-house developed tooling and platform software developed by Exoscale's EU-based engineering team. Top languages and large repo count demonstrate significant software development. - Exoscale Jobs – Engineering Roles in Europe other 3. September 2026
Job listings for SREs, hardware engineers, and capacity planners based in Madrid, Munich, and Lausanne with EU remote option.
Relevance: Demonstrates that core software development positions are based in EU countries, supporting the finding that essential parts are designed and maintained by EU teams.
All possible answer options (4)
- 2. Software is of foreign origin with partial disclosure on its development (value 35.00, SEAL 2)
- 3. Core and essential parts of the software are designed and maintained by EU teams (value 71.00, SEAL 3) ✓
- 4. A large majority of the software is designed and maintained by EU teams (value 107.00, SEAL 3)
- 5. The software is exclusively designed and maintained by EU teams (value 143.00, SEAL 4)
Selected answer: 5. EU control and EU policy gates - As (4), plus EU-based compliance/security gates enforced in the pipeline (e.g., signing under your control, vulnerability checks, segregation of duties, auditable approvals) Value 143 SEAL 4
Notes: Exoscale's EU-based teams manage packaging, distribution & updates. SOC 2 Type 2 + ISO 27001 + audit trails enforce compliance/security gates (vuln checks, segregation of duties, auditable approvals) in the EU.
Evidence
- A1 Digital European Cloud other 3. September 2026
A1 Digital product page for Exoscale claiming 100% European cloud, data centers in EU, and exemption from US CLOUD Act.
Relevance: Confirms EU-based build and release operations on open-source technology with no external IP dependencies, verifying EU control and execution of software packaging and distribution. - SOC 2 Compliance | Exoscale other 3. September 2026
Exoscale holds a SOC 2 Type 2 report (available since 2023) verified by an independent CPA firm, covering Security, Availability, Processing Integrity, Confidentiality, and Privacy controls.
Relevance: SOC 2 Type 2 demonstrates enforced compliance/security gates (segregation of duties, vulnerability checks, auditable approvals) in Exoscale's EU-based software pipeline, meeting Option 5 criteria. - Sovereign Cloud and Data Sovereignty: An Overview — Exoscale Blog other 3. September 2026
Detailed blog post explaining EU Cloud Sovereignty Framework, distinction between data sovereignty and data residency, and why US hyperscalers cannot guarantee EU sovereignty due to CLOUD Act.
Relevance: Directly addresses supply chain sovereignty, emphasizing Exoscale's EU-only operations, no extra-territorial jurisdiction exposure, and software/infrastructure origin within Europe.
All possible answer options (4)
- 2. EU control, non-EU execution - Execution is performed by non-EU teams, but pipeline administration and final release approvals are under EU jurisdiction (value 35.00, SEAL 1)
- 3. Non-EU control, EU execution - Execution is performed by EU teams, but pipeline administration and/or final release approvals (incl. signing) are under non-EU jurisdiction (value 71.00, SEAL 3)
- 4. EU control & execution - Build/release/deployment is executed by EU teams and governed from within the EU (pipeline administration, signing, approvals) (value 107.00, SEAL 3)
- 5. EU control and EU policy gates - As (4), plus EU-based compliance/security gates enforced in the pipeline (e.g., signing under your control, vulnerability checks, segregation of duties, auditable approvals) (value 143.00, SEAL 4) ✓
Selected answer: Few non-EU vendors or facilities involved in critical services, non documented, or non-EU vendors/facilities transparently documented Value 71 SEAL 2
Notes: Few non-EU critical deps (NVIDIA GPUs, Equinix datacenters) — most documented; hardware vendors not formally disclosed as supply-chain transparency
Evidence
- European GPU Clouds: 8 Alternatives to AWS and Azure for AI Workloads other 3. September 2026
Comparison article listing Exoscale among EU cloud providers, noting NVIDIA dependency and sovereignty ranking.
Relevance: Identifies NVIDIA as structural non-EU hardware dependency for all EU providers including Exoscale, framing it as critical-service non-EU dependency lack of EU alternatives. - Exoscale — Compliance other 3. September 2026
Exoscale compliance hub detailing certifications, data center operators (A1 Telekom Austria Group + Equinix), and supplier compliance requirements.
Relevance: Transparently documents non-EU facility vendor (Equinix, US-HQ) for critical data center services in CH/FR/DE locations, with ISO certification requirements for suppliers. - Exoscale GPU Cloud Servers other 3. September 2026
GPU instances using NVIDIA B300, RTX Pro 6000 Blackwell, A40, A30, A5000, Tesla V100, RTX 3080 Ti. NGC integration, TensorFlow/PyTorch support out of the box.
Relevance: Shows full GPU hardware dependency on NVIDIA (US-headquartered, non-EU) for critical AI compute services — a key non-EU proprietary technology dependency.
All possible answer options (4)
- Mostly non-EU vendors or facilities involved in critical services, non documented (value 35.00, SEAL 1)
- Few non-EU vendors or facilities involved in critical services, non documented, or non-EU vendors/facilities transparently documented (value 71.00, SEAL 2) ✓
- Few non-EU vendors or facilities involved in non-critical services, documented (value 107.00, SEAL 3)
- No depedency on non-EU vendor or facility (value 143.00, SEAL 4)
Selected answer: Critical suppliers and subcontractors can be audited Value 71 SEAL 2
Notes: Exoscale's ISMS framework covers supplier risk and audit rights focused on critical/data center operators; no evidence of end-to-end audit rights across all sub-suppliers.
Evidence
- Exoscale — Compliance other 3. September 2026
Exoscale compliance hub detailing certifications, data center operators (A1 Telekom Austria Group + Equinix), and supplier compliance requirements.
Relevance: Shows critical supplier naming/auditing (A1, Equinix) with compliance reviews but limited to critical suppliers; no broader sub-supplier chain audit rights. - How to Implement ISO 27001 Annex A 5.19 for Supplier Security other 3. September 2026
Guide implementing ISO 27001 Annex A 5.19-5.23: supplier classification, audit rights clauses in contracts, subcontractor mapping, and ongoing supplier security risk management.
Relevance: Explains how ISO 27001 (Exoscale's ISMS) mandates audit rights clauses for high-risk/critical suppliers while second-tier subcontractors lack visibility—supporting critical-supplier focus. - Sovereign Cloud and Data Sovereignty: An Overview — Exoscale Blog other 3. September 2026
Detailed blog post explaining EU Cloud Sovereignty Framework, distinction between data sovereignty and data residency, and why US hyperscalers cannot guarantee EU sovereignty due to CLOUD Act.
Relevance: Explicitly lists supply chain transparency and audit rights as requirement but does not demonstrate Exoscale provides audit rights for all suppliers; aspirational not operational reality.
All possible answer options (4)
- Some suppliers and subcontractors can be audited (value 35.00, SEAL 1)
- Critical suppliers and subcontractors can be audited (value 71.00, SEAL 2) ✓
- Most suppliers and subcontractors can be audited (value 107.00, SEAL 3)
- All suppliers and subcontractors can be audited (value 143.00, SEAL 4)
SOV-6 — Technology Sovereignty
Technology sovereignty evaluates the degree of openness, transparency, and independence in the underlying technological stack, ensuring EU actors can interoperate, audit, and evolve solutions without lock-in to foreign proprietary systems.
Weight 15%
Selected answer: 3. Mixed (partial openness) - Key interfaces are documented and partly standards-based, but important functions or data formats remain proprietary/vendor-specific Value 100 SEAL 2
Notes: OpenAPI-spec APIs, S3-compatible storage, standard Kubernetes; but core compute, IAM, KMS, DBaaS APIs are vendor-specific. Mixed openness profile.
Evidence
- API v2 Introduction — OpenAPI Compliance Announcement other 3. September 2026
Changelog entry announcing API v2 compliance with the OpenAPI standard, with deprecated legacy API v1 sunset notice and client library availability.
Relevance: Confirms APIs follow OpenAPI doc standard with versioning, but the API itself is Exoscale-specific — not an internationally standardized cloud interface. - Exoscale AI Cloud Infrastructure other 3. September 2026
Exoscale AI suite: NVIDIA GPU instances, managed/dedicated inference for open-source Hugging Face models, vector databases — all hosted in European data centers.
Relevance: Explicit vendor statement on open standards adoption for some services, while other core APIs remain proprietary — supporting mixed openness assessment. - Exoscale API Reference Documentation other 3. September 2026
Official Exoscale API documentation published as OpenAPI specification (YAML/JSON), covering compute, SKS, DBaaS, S3-compatible object storage, KMS, IAM, and more.
Relevance: Shows APIs use OpenAPI format and S3-compatible storage, but core interfaces remain Exoscale-proprietary rather than international standards-based.
All possible answer options (4)
- 2. Restricted proprietary APIs - Some vendor APIs exist, but they are limited/restricted (access, scope, licensing) and interoperability remains vendor-controlled (value 50.00, SEAL 1)
- 3. Mixed (partial openness) - Key interfaces are documented and partly standards-based, but important functions or data formats remain proprietary/vendor-specific (value 100.00, SEAL 2) ✓
- 4. Standards-based and broadly compatible - Interfaces and data formats predominantly follow recognised open standards (e.g., ETSI/CEN/CENELEC, ISO/IEC, IETF/W3C) with stable versioning and full documentation (value 150.00, SEAL 3)
- 5. Open-by-default with portability - All critical functions are accessible via open, well-documented, non-proprietary APIs and standard formats, with published specifications and minimal vendor-specific dependencies enabling easy third-party integration (value 200.00, SEAL 4)
Selected answer: 4. Policy for most core services - A formal policy mandates and documents open standards for most core services, with managed exceptions Value 150 SEAL 3
Notes: Open standards systematically adopted across most core services (OpenAPI, S3, Kubernetes/CSI, KVM, CloudStack, standard export formats) though no single formal policy document is publicly published.
Evidence
- Apache CloudStack — Official Website other 3. September 2026
Official Apache CloudStack site describing it as an open-source IaaS cloud computing platform used by MSPs, telcos, and cloud providers with multi-hypervisor support and AWS API compatibility.
Relevance: Confirms Exoscale's infrastructure foundation is a fully open-source, standards-based platform — not proprietary — reducing vendor lock-in across core compute and orchestration layers. - Comparing European Cloud Providers and Open Source Alternatives to US Platforms other 4. September 2026
Third-party analysis positioning Exoscale among European providers built on open-source foundations (OpenStack, Kubernetes) and examining Gaia-X's use of open standards for federated infrastructure.
Relevance: Provides independent assessment of Exoscale's alignment with open standards and open-source infrastructure within the European cloud sovereignty context. - Exoscale API Reference Documentation other 3. September 2026
Official Exoscale API documentation published as OpenAPI specification (YAML/JSON), covering compute, SKS, DBaaS, S3-compatible object storage, KMS, IAM, and more.
Relevance: Demonstrates formal adoption of the OpenAPI standard across the entire platform API and S3-compatible storage interface, evidencing open standards compliance for core services.
All possible answer options (4)
- 2. Ad hoc use - Open standards are used inconsistently on a case-by-case basis, without documented rationale or governance (value 50.00, SEAL 0)
- 3. Partial core adoption - Open standards are used and documented for some core services, while other core services remain proprietary/vendor-specific (value 100.00, SEAL 2)
- 4. Policy for most core services - A formal policy mandates and documents open standards for most core services, with managed exceptions (value 150.00, SEAL 3) ✓
- 5. Policy for all core services - A formal policy mandates and documents open standards for all core services (value 200.00, SEAL 4)
Selected answer: 5. Fully open-source software is governed by an independent or EU-based entity, granting full rights to audit, modify, redistribute, and seamlessly transfer stewardship Value 200 SEAL 4
Notes: Core platform (Apache CloudStack, Kubernetes, KVM) is fully open source under independent foundations (ASF, CNCF). Exoscale's own SDKs/tools are Apache 2.0 on GitHub, granting full audit, modify, redistribute rights.
Evidence
- A Deep Dive into Exoscale SKS Internals other 3. September 2026
Technical blog revealing Exoscale's infrastructure is built on Apache CloudStack, an open-source IaaS platform, with Kubernetes, etcd, and cloud-init as core components.
Relevance: Demonstrates Exoscale's cloud platform is built entirely on open-source software with permissive licenses, ensuring transparency and adaptability of the underlying stack. - About Apache CloudStack other 4. September 2026
Apache CloudStack is a Top-Level Project of the Apache Software Foundation, governed by a PMC under 'The Apache Way' — a meritocratic, community-driven process.
Relevance: Confirms the core IaaS orchestration software Exoscale relies on is governed by an independent foundation (ASF), not a single company, enabling seamless stewardship transfer. - GitHub - exoscale/egoscale: Exoscale Go Bindings other 4. September 2026
Exoscale's official Go library on GitHub, licensed under Apache License 2.0, with 42 contributors and 1,156 commits. Actively maintained with v3 API.
Relevance: Shows Exoscale's own tooling is open source under Apache 2.0, granting full rights to audit, modify, and redistribute, supporting transparency and independence.
All possible answer options (4)
- 2. Source code is available for review but modification and handover rights are under very strict conditions (value 50.00, SEAL 2)
- 3. The software is open source , permitting modification and redistribution, but governance is centralised (e.g., single-company or non-open foundation), limiting strategic autonomy or smooth handover (value 100.00, SEAL 3)
- 4. The software is open source with significant EU contributions but governance is restricted and handover is possible (value 150.00, SEAL 4)
- 5. Fully open-source software is governed by an independent or EU-based entity, granting full rights to audit, modify, redistribute, and seamlessly transfer stewardship (value 200.00, SEAL 4) ✓
Selected answer: Large corpus of public insight exists (all) Value 150 SEAL 3
Notes: Exoscale publishes extensive architecture docs, data flows, open dependencies & 299 GitHub repos for full service transparency.
Evidence
- A Deep Dive into Exoscale SKS Internals other 3. September 2026
Technical blog revealing Exoscale's infrastructure is built on Apache CloudStack, an open-source IaaS platform, with Kubernetes, etcd, and cloud-init as core components.
Relevance: Directly demonstrates public visibility into architectural internals, dependencies, and service design of Exoscale's platform. - Exoscale Academy — Certified Solution Architect other 4. September 2026
Public training documentation covering IaaS+ platform architecture, data flows, storage encryption hierarchy, network architecture, and supply chain.
Relevance: Comprehensive public architectural documentation across compute, storage, networking, DBaaS layers and supplier chain — meets 'large corpus' criterion. - Exoscale GitHub Organization — Open-Source Repositories other 3. September 2026
299 public repositories including CLI (exo), Terraform provider, Go SDK (egoscale), Python SDK, Kubernetes CSI driver, Karpenter provider, and Cloud Controller Manager.
Relevance: 299 public repos provide deep visibility into Exoscale's technology stack, integration patterns, and APIs supporting architectural transparency.
All possible answer options (4)
- Insight accessible during audits (value 50.00, SEAL 2)
- Some public insight exists (all) (value 100.00, SEAL 3)
- Large corpus of public insight exists (all) (value 150.00, SEAL 3) ✓
- Customers can contribute to adapt and enhance the service (value 200.00, SEAL 4)
Selected answer: EU-hosted, foreign stack Value 50 SEAL 3
Notes: Exoscale hosts in EU DCs but uses entirely foreign processors (Intel/AMD) and NVIDIA GPUs. No EU-designed processors or accelerators in their HPC stack.
Evidence
- Advancing European Sovereignty in HPC with RISC-V (EuroHPC JU) other 31. August 2026
EuroHPC JU article on DARE project designing EU sovereign RISC-V HPC accelerators and processors with €120M budget.
Relevance: Shows EU is still building sovereign HPC processors; Exoscale does not participate or use these — confirming foreign stack dependence. - Exoscale GPU Cloud Servers other 3. September 2026
GPU instances using NVIDIA B300, RTX Pro 6000 Blackwell, A40, A30, A5000, Tesla V100, RTX 3080 Ti. NGC integration, TensorFlow/PyTorch support out of the box.
Relevance: Confirms complete dependency on NVIDIA (US) GPUs for HPC/AI workloads — no EU-designed accelerators used. - Sovereign Cloud and Data Sovereignty: An Overview — Exoscale Blog other 3. September 2026
Detailed blog post explaining EU Cloud Sovereignty Framework, distinction between data sovereignty and data residency, and why US hyperscalers cannot guarantee EU sovereignty due to CLOUD Act.
Relevance: Discusses technology sovereignty and contrasts EU-hosted infrastructure with continued foreign processor/hardware dependency — directly relevant to HPC sovereignty gap.
All possible answer options (4)
- EU-hosted, foreign stack (value 50.00, SEAL 3) ✓
- Co-designed or integrated in EU (value 100.00, SEAL 3)
- EU processor IP, non-EU fabs (value 150.00, SEAL 3)
- EU design + EU fab + EU ops (value 200.00, SEAL 4)
SOV-7 — Security & Compliance Sovereignty
Security & Compliance sovereignty measures the extent to which security operations, compliance obligations, and resilience measures are controlled within the EU , ensuring independence from foreign jurisdictions and long-term operational assurance.
Weight 15%
Selected answer: ELA3 Value 107 SEAL 3
Notes: Comprehensive EU+intl certifications (ISO 27001/27017/27018, BSI C5, HDS, TISAX, SOC 2) but Swiss HQ and no SecNumCloud/EUCS limit full EU sovereignty.
Evidence
- Exoscale — Compliance other 3. September 2026
Exoscale compliance hub detailing certifications, data center operators (A1 Telekom Austria Group + Equinix), and supplier compliance requirements.
Relevance: Provides authoritative detail on each certification's type, scope, and latest revision — essential for verifying EU vs international certification completeness. - Exoscale BSI C5 Compliance Page other 4. September 2026
Dedicated page for Exoscale's BSI C5 Type 2 attestation explaining the German government cloud security standard and its significance for EU compliance.
Relevance: BSI C5 is a key EU-recognized certification; its presence strengthens the security & compliance sovereignty assessment for EU-specific context. - Exoscale Compliance Hub other 4. September 2026
Main compliance page listing ISO 27001/27017/27018, SOC 2, BSI C5, HDS, TISAX, GDPR, HIPAA certifications and data center certifications.
Relevance: Lists all EU and international security certifications attained by Exoscale, directly supporting the assessment question on certification breadth.
All possible answer options (4)
- ELA1 (value 35.00, SEAL 1)
- EAL2 (value 71.00, SEAL 2)
- ELA3 (value 107.00, SEAL 3) ✓
- EAL4-5 (value 143.00, SEAL 4)
Selected answer: 4. Partial compliance to most of the well-known EU Regulations (requirements implemented and operational with minor exceptions) Value 107 SEAL 4
Notes: GDPR directly addressed; NIS2/DORA supported via ISO 27001, SOC 2, BSI C5 audits but not independently attested. Minor gaps remain.
Evidence
- Exoscale — Compliance other 3. September 2026
Exoscale compliance hub detailing certifications, data center operators (A1 Telekom Austria Group + Equinix), and supplier compliance requirements.
Relevance: Lists all independently audited certifications and explicitly references DORA support, showing operational compliance controls for EU regulatory frameworks including GDPR-adjacent standards. - Exoscale Compliance Hub other 4. September 2026
Main compliance page listing ISO 27001/27017/27018, SOC 2, BSI C5, HDS, TISAX, GDPR, HIPAA certifications and data center certifications.
Relevance: Demonstrates independently audited compliance with multiple security and data protection frameworks relevant to GDPR and EU regulatory adherence, mapped via a 32-domain Secure Control Framework. - Sovereign Cloud and Data Sovereignty: An Overview — Exoscale Blog other 3. September 2026
Detailed blog post explaining EU Cloud Sovereignty Framework, distinction between data sovereignty and data residency, and why US hyperscalers cannot guarantee EU sovereignty due to CLOUD Act.
Relevance: Shows Exoscale's understanding of and positioning against NIS2 and DORA requirements, explaining how EU-based providers support customer compliance obligations under these frameworks.
All possible answer options (4)
- 2. Limited compliance to some well-known EU Regulations (basic practices exist but informal, incomplete, or non-systematic) (value 35.00, SEAL 4)
- 3. Moderate compliance to some well-know EU Regulations (controls exist but gaps remain; compliance not fully demonstrated) (value 71.00, SEAL 4)
- 4. Partial compliance to most of the well-known EU Regulations (requirements implemented and operational with minor exceptions) (value 107.00, SEAL 4) ✓
- 5. Fully compliant to all well-know EU regulations (verified compliance, independently audited) (value 143.00, SEAL 4)
Selected answer: 3. The primary SOC is in the EU but incidents may be escalated to non-EU teams Value 71 SEAL 1
Notes: EU-based SOC in Vienna handles primary incident response, but deep remediation escalates to Mandiant (US). No evidence of ENISA participation.
Evidence
- A1 Digital – Cyber Defense Solutions other 4. September 2026
A1 Digital's official page detailing their 24/7 Security Operations Center based in Vienna, Austria, with incident response and managed security services.
Relevance: Confirms A1 Digital (Exoscale's parent) operates a 24/7 SOC in Vienna (EU), handling primary incident detection and response for European customers. - A1 Group – Information Security other 4. September 2026
A1 Group's corporate security page describing A1-CERT as a FIRST member since 2023, NIS compliance since 2020, and ISO 27001/27011/20000 certifications.
Relevance: Confirms EU-based CERT operations in Austria with FIRST membership. NIS compliance situates incident handling under EU jurisdiction but FIRST enables global coordination. - IKARUS Security – A1 Digital Success Story other 4. September 2026
Case study confirming A1 Digital's data sovereignty in Austria and use of Mandiant specialists for deep incident remediation.
Relevance: Confirms all data stays in Austria (EU) but deep remediation is escalated to Mandiant (US-based), establishing a non-EU escalation path for complex incidents.
All possible answer options (4)
- 2. A hybrid model is used with SOC functions split between EU and non-EU locations (value 35.00, SEAL 1)
- 3. The primary SOC is in the EU but incidents may be escalated to non-EU teams (value 71.00, SEAL 1) ✓
- 4. The entire incident lifecycle is handled by teams operating exclusively within the EU. Threat intelligence and incident data obtained mostly via EU sources (value 107.00, SEAL 3)
- 5. The full incident lifecycle is handled by EU-based teams with active participation in ENISA's information sharing frameworks. Threat intelligence and incident data are gathered worldwide (value 143.00, SEAL 4)
Selected answer: 4. Customers have full direct access to their security monitoring and logs which are stored in the EU Value 107 SEAL 3
Notes: Customers have full direct access to security monitoring/logs via Portal, CLI, API, and webhook forwarding. All zones in Europe. No WORM immutability, so Option 5 not met.
Evidence
- Audit Trail — Exoscale Community Documentation other 3. September 2026
Exoscale's Audit Trail tracks all security-relevant user activity and API usage. Events include origin, owner, and resource details. Short-term retention 30 days; long-term stored in customer's own SOS bucket (daily uploads, 2-hour event windows).
Relevance: Shows customers have full direct access to security logs via Portal, CLI, and API. All data stored in European data centers. Append-only long-term storage but not strictly immutable/WORM. - Kubernetes Audit Log Available on Exoscale SKS — Exoscale Blog other 3. September 2026
Exoscale SKS supports forwarding Kubernetes API Server audit logs to a customer-configured webhook endpoint, enabling real-time security analysis with tools like Falco. Full customer control over audit data destination.
Relevance: Demonstrates full customer control over K8s audit log routing and real-time security monitoring via Falco. Configurable directly in Exoscale Portal. - SOS Data Events for Audit-Trail other 4. September 2026
Documentation on per-bucket object storage API request logs delivered to customer webhooks with HMAC-SHA256 signatures for tamper verification.
Relevance: Shows detailed audit logging with cryptographic HMAC-SHA256 signatures for tamper-proof verification, delivered directly to customer-controlled webhooks. Supports Option 4 but no strict immutability (WORM).
All possible answer options (4)
- 2. Customers receive periodic reports based on security logs (value 35.00, SEAL 1)
- 3. Customers have access to a basic portal for monitoring (value 71.00, SEAL 1)
- 4. Customers have full direct access to their security monitoring and logs which are stored in the EU (value 107.00, SEAL 3) ✓
- 5. Customers have full access to immutable tamper-proof logs stored exclusively within the EU (value 143.00, SEAL 4)
Selected answer: 3. Moderate compliance - GDPR/NIS2-aligned reporting procedures in place with vulnerabilities and breaches communicated within mandated timelines; CSIRT cooperation available but not real-time Value 71 SEAL 2
Notes: GDPR/NIS2-aligned via ISO 27001 & A1 Digital NIS2 readiness; A1-CERT/FIRST enables CSIRT cooperation but no real-time EU CSIRT data sharing evidenced.
Evidence
- Cloud Security | How Exoscale Keeps Your Data Safe other 3. September 2026
Exoscale security page detailing ISO 27001-certified datacenters, drive decommissioning, and Swiss data protection laws.
Relevance: Shows proactive vulnerability disclosure via bug bounty and PGP security contact, supporting moderate compliance level. - GDPR Compliance — Exoscale other 3. September 2026
Exoscale's official GDPR compliance page confirming its Swiss incorporation, jurisdiction, and that as a European entity with no US parent it is not subject to the CLOUD Act.
Relevance: Confirms GDPR-aligned reporting framework; notification responsibility model shows aligned but customer-facing disclosure approach. - NIS2: Meaning, Requirements & Sectors | A1 Digital other 4. September 2026
A1 Digital's NIS2 knowledge hub detailing 24h/72h/1-month incident reporting timelines and compliance requirements.
Relevance: Parent company demonstrates NIS2-aligned reporting timelines awareness and compliance consulting readiness for incident disclosure.
All possible answer options (4)
- 2. Limited compliance - reporting is reactive with limited transparency and unguaranteed timelines; CSIRT cooperation possible on best-effort basis (value 35.00, SEAL 1)
- 3. Moderate compliance - GDPR/NIS2-aligned reporting procedures in place with vulnerabilities and breaches communicated within mandated timelines; CSIRT cooperation available but not real-time (value 71.00, SEAL 2) ✓
- 4. Partial compliance - there is a monitored reporting flow with internal SLAs equal or below regulatory maximums; contractually prepared to support EU-directed investigations; data sharing with EU CSIRTs available but not in real-time (value 107.00, SEAL 3)
- 5. Full compliance - full EU-compliant breach disclosure with real-time data sharing to EU CSIRTs with audit-backed processes, proactive vulnerability disclosure and threat intel sharing; proven readiness for investigations (value 143.00, SEAL 4)
Selected answer: 3. Moderate Autonomy - security patches are deployed with sufficient notice to the customer and testing is possible, except for zero-day patching Value 71 SEAL 4
Notes: Platform patches follow Exoscale's schedule with changelog notice. IaaS customers independently test/patch guest OS. Zero-day platform patches lack advance notice. EU-based vendor, no non-EU dependency.
Evidence
- Exoscale Changelog – Platform Updates & Security Patches other 4. September 2026
Exoscale's public changelog tracking ongoing platform maintenance, security patches, Kubernetes version updates, and OS template updates with dates and details.
Relevance: Demonstrates that platform patches are published with notice and documentation, allowing customers to test ahead of changes but with zero-day patches applied urgently without advance warning. - Exoscale Compliance Hub other 4. September 2026
Main compliance page listing ISO 27001/27017/27018, SOC 2, BSI C5, HDS, TISAX, GDPR, HIPAA certifications and data center certifications.
Relevance: Lists Vulnerability & Patch Management and Security Operations as defined control domains, confirming structured patch management processes with notice mechanisms and testing controls. - Exoscale Shared Responsibility Model other 4. September 2026
Official Exoscale documentation defining the shared responsibility model for IaaS and DBaaS, detailing who handles vulnerability management and patching at each layer.
Relevance: Shows platform patching is Exoscale's responsibility (vendor-scheduled) while guest OS patching is the customer's responsibility, defining autonomy boundaries for security patch deployment.
All possible answer options (4)
- 2. Limited Autonomy - security patches are deployed according to vendor schedules; basic testing is possible (value 35.00, SEAL 1)
- 3. Moderate Autonomy - security patches are deployed with sufficient notice to the customer and testing is possible, except for zero-day patching (value 71.00, SEAL 4) ✓
- 4. High Autonomy - security patches can be deployed independently by the customer, without customers' checks (value 107.00, SEAL 4)
- 5. Full Autonomy - security patches can be deployed independently by the customer, with customers' checks (value 143.00, SEAL 4)
Selected answer: 4. High control by independent entities to request data from the vendor Value 107 SEAL 1
Notes: DPA grants audit rights (annual, 30d notice, NDA) plus Compliance Center self-service access to third-party reports; not unrestricted, so not full control.
Evidence
- Exoscale — Compliance other 3. September 2026
Exoscale compliance hub detailing certifications, data center operators (A1 Telekom Austria Group + Equinix), and supplier compliance requirements.
Relevance: Shows independent auditors' reports are available on demand, but gated by NDA and portal access—not fully open to any entity without contract. - Exoscale Data Processing Addendum (DPA) other 4. September 2026
Full DPA with Section 10 defining customer audit rights: annual, 30-day notice, mutually agreed scope, NDA required.
Relevance: DPA Section 10 explicitly codifies audit rights and constraints, showing EU entities have structured but circumscribed audit access—high control, not full unrestricted. - SOC 2 Compliance | Exoscale other 3. September 2026
Exoscale holds a SOC 2 Type 2 report (available since 2023) verified by an independent CPA firm, covering Security, Availability, Processing Integrity, Confidentiality, and Privacy controls.
Relevance: Demonstrates regular independent third-party audits accessible to customers, supporting high but controlled auditability rather than unrestricted access.
All possible answer options (4)
- 2. Limited access to independent entities to the data provided by the vendor (value 35.00, SEAL 1)
- 3. Partial control by independent entities on the data provided by the vendor (value 71.00, SEAL 1)
- 4. High control by independent entities to request data from the vendor (value 107.00, SEAL 1) ✓
- 5. Full control by any idependent entity to perform security and compliance audits (value 143.00, SEAL 4)
SOV-8 — Environmental Sustainability
Environmental sustainability assesses autonomy and resilience of cloud services over the long term in relation to energy usage, dependency and raw material scarcity.
Weight 5%
Selected answer: PUE < 1.5 + roadmap Value 125 SEAL 4
Notes: Exoscale's data center partners (A1 Vienna PUE ≤ 1.4, Equinix PUE ~1.37) are below 1.5, with carbon neutrality roadmap to 2030 and energy efficiency targets.
Evidence
- A1 & Exoscale Open Second Public Cloud Zone in Vienna other 3. September 2026
Press release on €40M A1 datacenter investment in Vienna, Tier III facility with 2,550m² white space, connected load 12MW.
Relevance: Provides verified PUE data for Exoscale's Austrian data center zones, confirming PUE < 1.5 at parent's flagship facility. - Equinix Environmental Sustainability other 4. September 2026
Equinix sustainability page reporting global average PUE of 1.37 (2025), 100% renewable coverage in EMEA, net-zero target by 2040, and PUE roadmap to 1.33 by 2030.
Relevance: Equinix hosts Exoscale's Swiss and German zones; their PUE ~1.37 and efficiency roadmap support the PUE < 1.5 + roadmap assessment. - Sustainability | Exoscale other 3. September 2026
Details Exoscale's green strategy: 100% renewable energy in DE/CH/AT, carbon neutrality target 2030, ISO-compliant life cycle assessments, CSRD reporting.
Relevance: Direct evidence of Exoscale's energy efficiency measures and sustainability roadmap, confirming measurable improvement targets but no explicit PUE disclosure.
All possible answer options (5)
- PUE > 0 (value 0.00, SEAL 1)
- PUE < 3 (value 62.00, SEAL 1)
- PUE < 1.5 + roadmap (value 125.00, SEAL 4) ✓
- PUE < 1.3 (value 187.00, SEAL 4)
- PUE < 1.2 EU verified (value 250.00, SEAL 4)
Selected answer: Documented program Value 125 SEAL 3
Notes: Exoscale documents circular economy practices: server reuse, refurbishment, and ISO 14000 LCA, but lacks explicit EU circular economy regulatory alignment or certification.
Evidence
- A1 Digital European Cloud other 3. September 2026
A1 Digital product page for Exoscale claiming 100% European cloud, data centers in EU, and exemption from US CLOUD Act.
Relevance: Corporate-level sustainability context: confirms Exoscale's sustainability strategy within A1 Group, including impact reporting, but no detail on EU-certified hardware lifecycle. - E-Waste Recycling & IT Equipment Recycling Services | SK Tes other 4. September 2026
Industry e-waste recycling service covering WEEE Directive compliance, server lifecycle, data sanitization, and circular economy model for IT hardware.
Relevance: Provides benchmark for EU-aligned e-waste and WEEE compliance standards that cloud providers should reference; Exoscale does not cite such frameworks explicitly. - Sustainability | Exoscale other 3. September 2026
Details Exoscale's green strategy: 100% renewable energy in DE/CH/AT, carbon neutrality target 2030, ISO-compliant life cycle assessments, CSRD reporting.
Relevance: Directly documents circular economy practices for hardware: reuse, refurbishment, and LCA from raw materials to disposal. Lacks explicit EU regulatory framework alignment.
All possible answer options (5)
- No policy (value 0.00, SEAL 0)
- Circular economy EU-aligned (value 62.00, SEAL 0)
- Documented program (value 125.00, SEAL 3) ✓
- Circular economy EU-aligned (value 187.00, SEAL 4)
- EU-certified lifecycle (value 250.00, SEAL 4)
Selected answer: Detailed EU methodology Value 187 SEAL 3
Notes: Exoscale uses ISO 14000 LCA, aligns with CSRD/ESRS via A1 Group, and provides per-zone carbon data—detailed EU methodology but no evidence of EU audit.
Evidence
- A1 Group — Policies, Guidelines and Reports other 4. September 2026
A1 Group's ESG hub with annual Sustainability Statements (ESRS/CSRD), E-KPI factsheets, Environmental Policy, and Clean Energy Strategy.
Relevance: Parent organization A1 Group publishes annual ESRS/CSRD-compliant sustainability reports covering Scope 1-3 emissions, energy, and water—EU methodology applied group-wide. - Environmental Impact — Exoscale Documentation other 4. September 2026
Exoscale's environmental impact reporting via console and API, using LCA methodology with indicators like GWP, acidification, and eutrophication.
Relevance: Details Exoscale's technical reporting infrastructure providing transparent, granular environmental impact data using ADEME/ISO-based LCA methodology aligned with EU standards. - Sustainability | Exoscale other 3. September 2026
Details Exoscale's green strategy: 100% renewable energy in DE/CH/AT, carbon neutrality target 2030, ISO-compliant life cycle assessments, CSRD reporting.
Relevance: Shows Exoscale uses detailed EU-aligned methodology (CSRD, ISO 14000 LCA) for environmental impact measurement and reporting with transparent per-zone carbon data.
All possible answer options (5)
- No reporting (value 0.00, SEAL 1)
- Detailed EU methodology (value 62.00, SEAL 1)
- Annual report (value 125.00, SEAL 2)
- Detailed EU methodology (value 187.00, SEAL 3) ✓
- EU-audited reporting (value 250.00, SEAL 4)
Selected answer: Mix of EU and non-EU supplies Value 125 SEAL 4
Notes: Swiss data centers use non-EU energy; EU sites (Bulgaria 75%, Croatia 91% renewable) aren't fully green. Mix of EU/non-EU supplies.
Evidence
- Exoscale Data Centers in Switzerland: Zurich & Geneva other 4. September 2026
Details Swiss data center zones hosted at Equinix, both powered by 100% renewable energy with green energy certificates.
Relevance: Confirms Swiss (non-EU) data centers powered by Swiss-sourced renewable energy, demonstrating non-EU energy supplies in Exoscale's infrastructure. - Exoscale Zones in Bulgaria other 4. September 2026
Official page for BG-SOF-1 zone in Sofia, hosted by A1 Bulgaria, with facility certifications and infrastructure details.
Relevance: Confirms Bulgarian (EU) data center where only 75% of energy is renewable, showing EU-sourced energy that is not fully green, supporting mix classification. - Sustainability | Exoscale other 3. September 2026
Details Exoscale's green strategy: 100% renewable energy in DE/CH/AT, carbon neutrality target 2030, ISO-compliant life cycle assessments, CSRD reporting.
Relevance: Shows energy sourcing by zone, revealing Swiss (non-EU) data centers and non-fully-renewable EU sites in Bulgaria and Croatia, confirming a mix of EU and non-EU energy supplies.
All possible answer options (4)
- Only EU energy supplies (value 62.00, SEAL 4)
- Mix of EU and non-EU supplies (value 125.00, SEAL 4) ✓
- Only EU energy supplies (value 187.00, SEAL 4)
- Only green EU energy supplies (value 250.00, SEAL 4)
Data Centres
Exoscale has data centres in Switzerland, Austria, Germany, Croatia and in Bulgaria. According to Exoscale “Several peering connections with major local actors grant first in class performance in our geographical area”. The data centres are:
| Country | City | Name |
|---|---|---|
 Germany | Munich | DE-MUC-1 |
 Bulgaria | Sofia | BG-SOF-1 |
 Croatia | Zagreb | HR-ZAG-1 |
 Switzerland | Zurich | CH-DK-2 |
| Switzerland | Geneva | CH-GVA-2 |
 Austria | Vienna | AT-VIE-1 |
| Austria | Vienna | AT-VIE-2 |
| Germany | Frankfurt | DE-FRA-1 |
More information about the data centres can be found here: Exoscale Data Centres. A map with the geograpical location of the data centres can be found here.
Environmental Policy
Exoscale is basing its environmental policy on several measures
- Renewable Energy
- High Density Rack Design
- Refurbished Equipment
- Extended Server Fleet Life
- Energy-Efficient Design
- Direct Shipping
- Work Policies
All the details about the Exoscale environmental policy are documented on the Exoscale Sustainability page.
Certifications
Over the course of their history, Exoscale have managed to obtain a large number of certifications. These include the basic security certifications as well as a few special, industry-specific ones, such as HDS, TISAX and HIPAA.
 BSI C5
 CSA STAR
 HDS
 ISO 27001
 SOC 2
 TISAX
All the certifications, standards and frameworks that Exoscale complies with are listed on the Exoscale Compliance page.
Conclusion
As they claim themselves, Exoscale are offering a solid cloud platform. They have a good distribution of data centers to fulfill data residency and geo-redundancy requirements.
Regarding features and services, the Exoscale offering is a solid IaaS range but does not stick out compared to other players. Higher-level services are absent completely as of now and require a lot of platform work by the customer (with the notable exception of a managed Kafka service – something that many others are not offering).
A positive twist to this is that the Exoscale services are “just” repackaged Open Source – it should be relatively easy to move in and out and mix and match with Exoscale.
Resources
Compare with another provider
- HeadquartersLausanne, Switzerland
- Parent companyA1 Digital International GmbH & Co KG
- Cloud since2013
- ISINAT0000720008
- Websitewww.exoscale.com